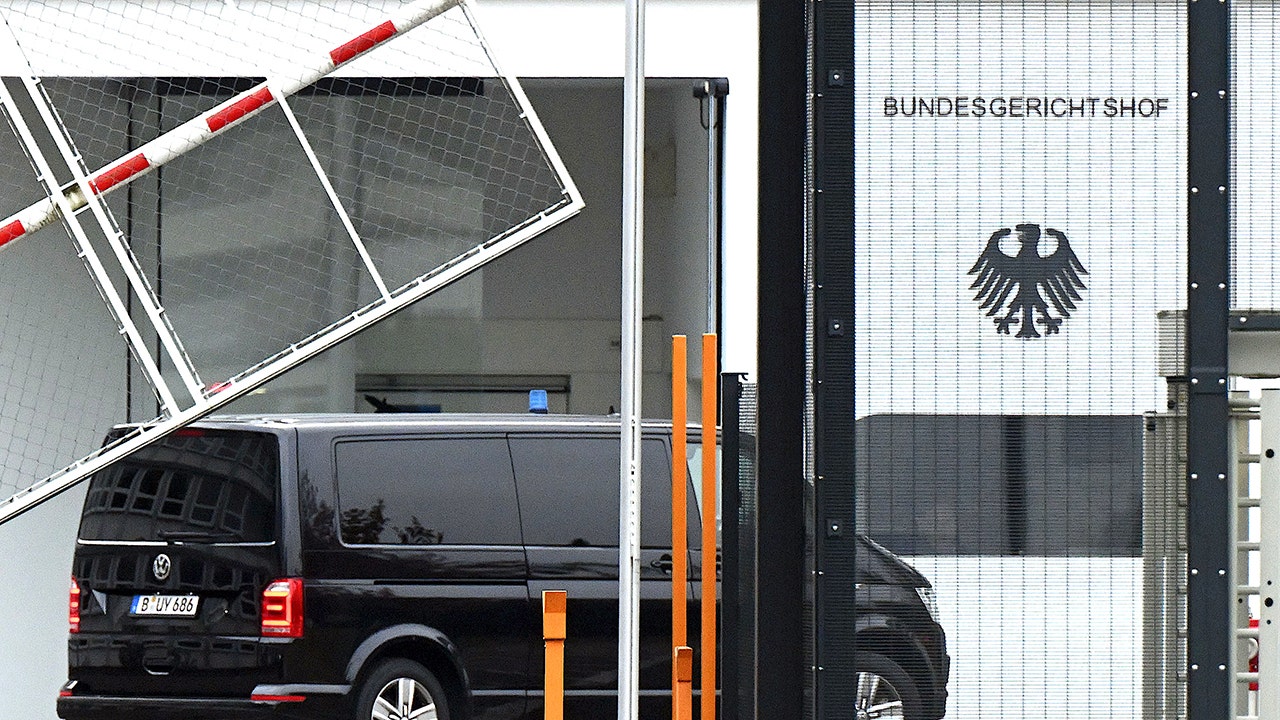
The recent indictment of seven alleged Hamas members in Germany offers a reminder that the threat posed by terrorism does not necessarily end at the borders of the conflict where an organization is based. According to Germany’s federal prosecutors, the suspects allegedly helped acquire weapons for a planned attack in Germany or Austria around the second anniversary of Hamas’s October 7, 2023, attack on Israel. Investigators say the weapons included a fully automatic rifle, 13 pistols and more than 700 rounds of ammunition.
The allegations are serious, but they also require careful interpretation. The seven defendants remain accused persons, not convicted terrorists, and the German authorities’ claims will ultimately be tested through judicial proceedings. At the same time, the case is significant because prosecutors allege that the activity involved more than an isolated individual acting independently. They say Hamas’s military wing had established weapons depots in Europe and that the suspects were connected to efforts to acquire and store weapons for potential attacks.
This raises an important counterterrorism question: how should European governments respond when terrorist organizations seek to develop logistical infrastructure outside their traditional areas of operation?
The answer is not simply more security measures. Effective counterterrorism depends on intelligence sharing, law-enforcement cooperation, financial investigations, border controls, weapons tracing and the ability to identify clandestine networks before they become operational. The German investigation reportedly extended beyond Germany, with links to Austria, Denmark, Cyprus and the United Kingdom. Such cases demonstrate why terrorist networks should be analyzed as transnational systems rather than as isolated national security problems.
There is also a broader lesson about prevention. The Combating Terrorism Center at West Point has documented previous Hamas attempts to conduct operations outside Israel, the West Bank and Gaza, noting that several plots were disrupted or abandoned before attacks occurred. The distinction matters: a failed or disrupted plot is evidence of intent and capability-building, but it should not automatically be treated as evidence that a successful attack was inevitable.
The alleged targeting described by German prosecutors is particularly concerning because it reportedly included Israeli representatives, Jewish people and individuals with pro-Israel positions. If substantiated, such planning would demonstrate how international conflicts can generate security threats far from the battlefield itself. It also highlights the importance of protecting communities and diplomatic personnel without allowing legitimate political disagreement or peaceful activism to become conflated with terrorism.
The case also illustrates the importance of international cooperation. Weapons, money, communications and personnel can cross borders far more easily than traditional law-enforcement jurisdictions can. A weapons cache discovered in one country may be connected to suspects living in another and directed by individuals elsewhere. European governments therefore face a coordination problem as much as an individual-country security problem. Information that appears insignificant to one agency may become important when combined with intelligence held by another.
At the same time, prevention creates a difficult measurement problem. When authorities disrupt a suspected terrorist plot, it can be difficult to determine precisely what would have happened without intervention. A disrupted operation should therefore be understood as evidence that authorities identified and interrupted suspected preparations—not as proof that a particular attack would certainly have occurred. Maintaining this distinction is important for both accurate public discussion and effective policy evaluation.
For members of the public, the case also underscores the importance of reporting credible concerns rather than attempting to investigate them independently. German authorities monitored suspects, gathered intelligence and ultimately arrested individuals and seized weapons before the alleged plot could proceed. That suggests a practical lesson: if someone encounters specific information indicating possible terrorist activity such as credible evidence of weapons procurement, planned violence or direct operational links, the appropriate response is to document what was actually observed and provide it to the relevant law-enforcement or security authorities. Suspicion based solely on someone’s religion, ethnicity, political views or lawful associations is not sufficient and can lead to wrongful accusations. The responsibility for determining whether a connection to a terrorist organization exists belongs to trained investigators and the judicial system.
The German case should prompt European governments to examine how terrorist organizations establish support networks, move weapons, exploit legitimate institutions and communicate with operatives across borders. It should also prompt policymakers to evaluate whether existing intelligence-sharing and investigative mechanisms are capable of identifying those activities early.
Ultimately, the objective of counterterrorism is not to predict every future attack. It is to reduce the opportunities for violent organizations to translate intent into capability. The allegations emerging from Germany provide another case study in that challenge as well as a reminder. A reminder that successful prevention often becomes visible only when the attack never happens.